Robber

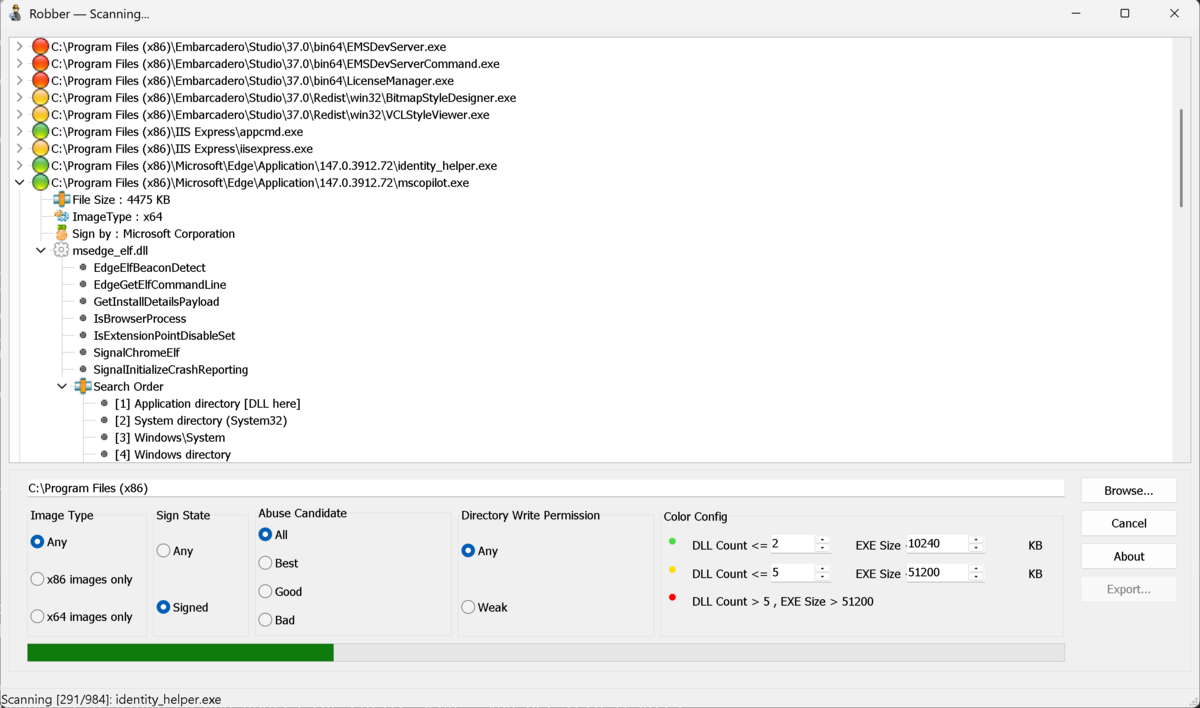
Robber is open source tool for finding executables prone to DLL hijacking
- Active
- Application
- Delphi
- GitHub
- ★ 799
- GPL-3.0


30,062 projects in the catalog.
Free Pascal, Lazarus and Delphi components, libraries and programs from GitHub, SourceForge, Codeberg, GitLab and more. Rate them, mark what looks interesting, and talk about them on their benches.
Robber is open source tool for finding executables prone to DLL hijacking
Windows utility designed to find code caves in x86 and x64 executables for code injection purposes.
Delphi open source show you how to code an Executable 32bit crypter with a simple Xor encryption.
Xbox Binary Strings Extractor is a proof-of-concept tool that dump all strings/pointer from a Xbox executable (usually default.xbe) to a CSV file.
Win32 Delphi applciation allows convienent editing of external signatures database in windows executable packer finder program PEID (http://peid.has.it/). Allows sorting, editing, adding, removal, searching and duplicate signature finding in "userdb.txt".
Library to create demo versions of your Delphi/FreePascal apps. Create versions that are time-limited, feature-limited, limited to a certain number of uses, etc. You could also protect executable from modification.
Security In the Online Package Manager
Unpacker for Clicklocker Protected Executables.
This version of OnGuard is port of Turbo Power OnGuard. OnGuard is a library to create demo versions of your Delphi, Kylix and Free Pascal applications. Create demo versions that are time-limited, feature-limited, limited to a certain number of uses, or limited to a certain number of concurrent network users. You could also protect executable file from modification, either by hacker or malware. Most functionality has been tested to work under Windows, Linux and FreeBSD.
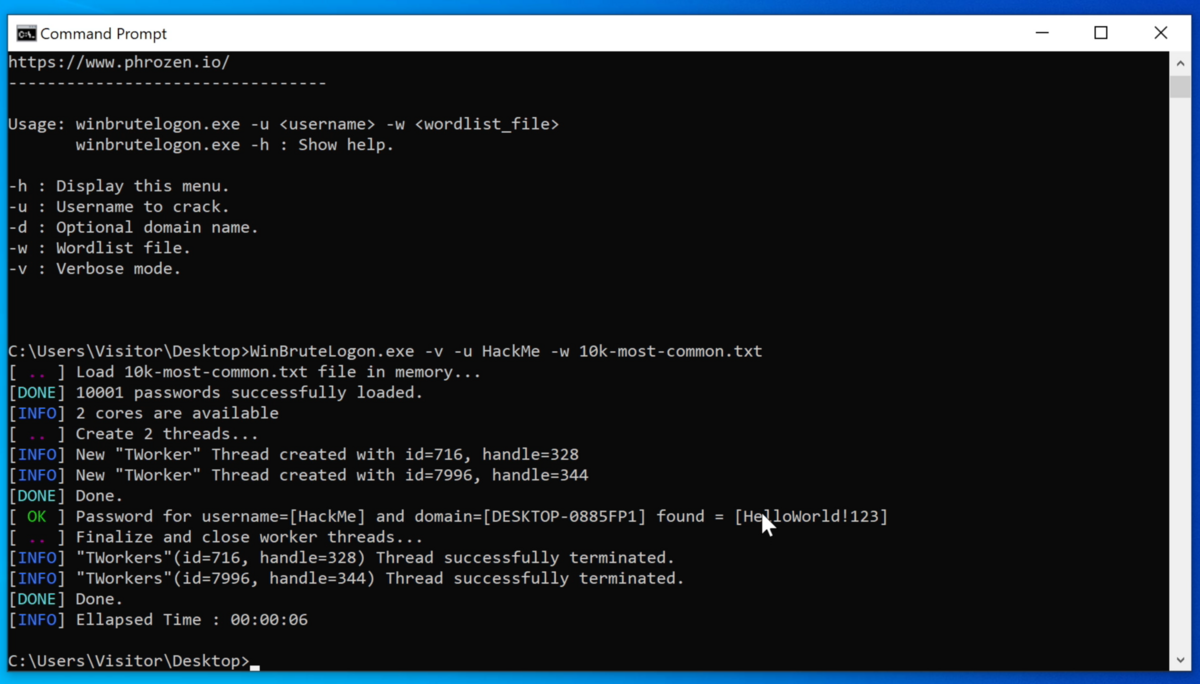
Crack any Microsoft Windows users password without any privilege (Guest account included)
Themida unpacker
An open-source, pentest and developer-oriented web browser, using the power of Lua
TaurusTLS is an Indy add-on that provides OpenSSL 3.x and 4.x support to Indy. It depends on IndyLaz.
Networking Security In the Online Package Manager
Multi platform toolkit for an interactive DNS shell commands exfiltration, by using DNS-Cat you will be able to execute system commands in shell mode over DNS protocol
An open-source notepad with features that are particularly useful to penetration testers
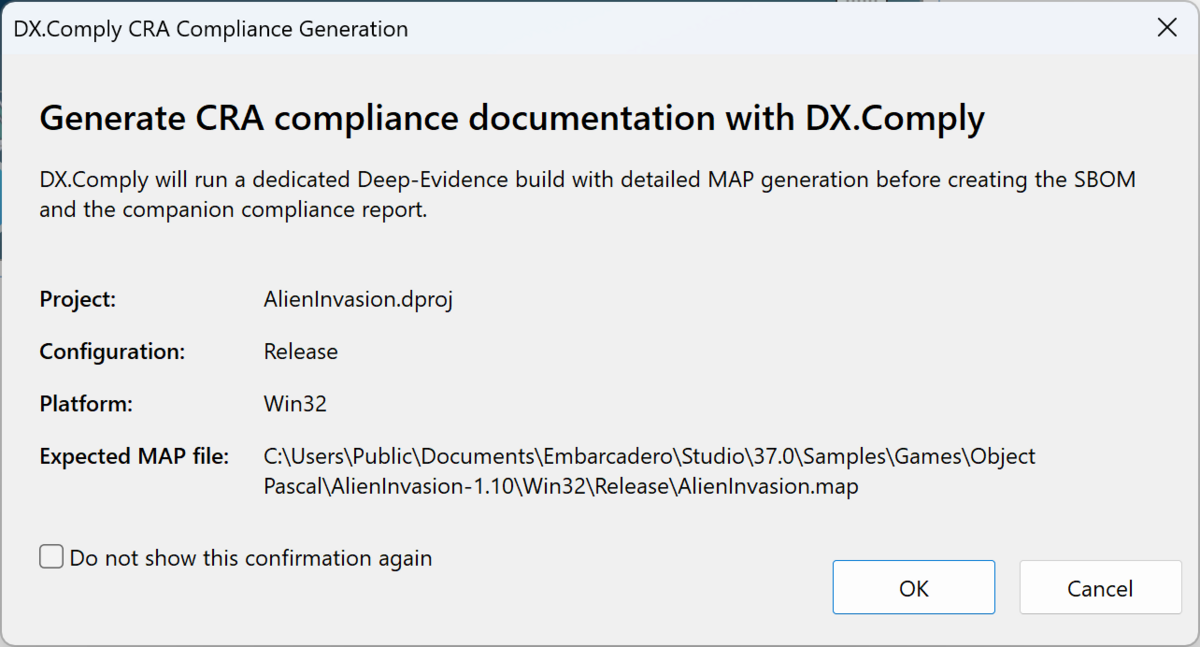
Generate CycloneDX SBOMs for Delphi projects — EU Cyber Resilience Act compliance in one click
An authorization library that supports access control models like ACL, RBAC, ABAC in Delphi
A collection of projects to augment the Indy project
Simple RunAs program for Windows.
NativePe: a PE loader/parser library for Delphi 12 (port of libpeconv, Win32 + Win64, open source)
SBOM generator tool for Delphi
Provides desktop based Linux users with a friendly GUI to break password protected PDF files
Thread hijacking
A Delphi-aware reverse-engineering toolkit — recover the class model from any Delphi PE, and unpack packed ones to get there.
An easy to use Drag and drop VCL Windows (WFP) Firewall component!
Go_VM — Delphi Go Source Virtualizer & Obfuscator
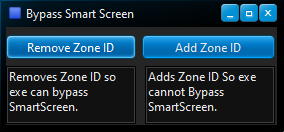
This project shows how to add and remove Zone ID's so that a PE Binary (.EXE) can run without triggering Microsoft Windows Smart Screen.
Delphi project to get and Decrypt Chrome encrypted passwords (Works on all chrome based Browsers)
An EXE Loader That Injects DLL at Entry Point
ImageHide is simple steganography tool using digital image files.
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
Execute Shellcode
Welcome to O2, a new way to store and organize your personal data.
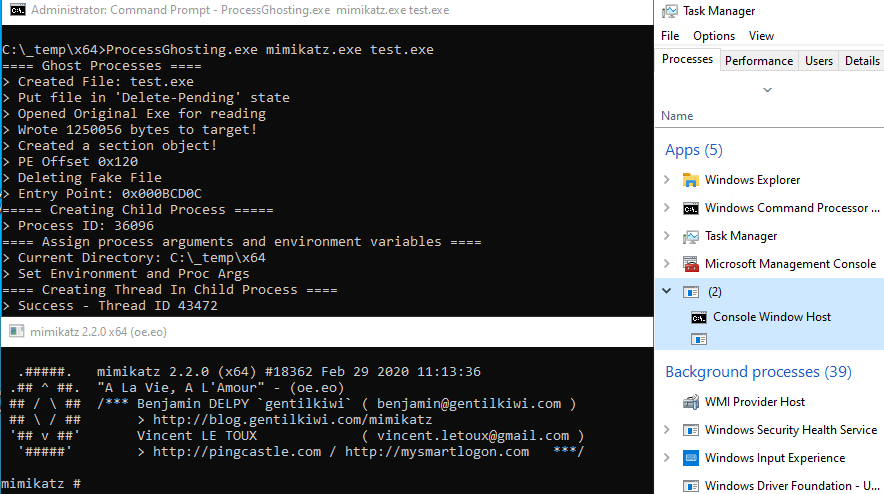
A Process Ghosting PoC written in Delphi
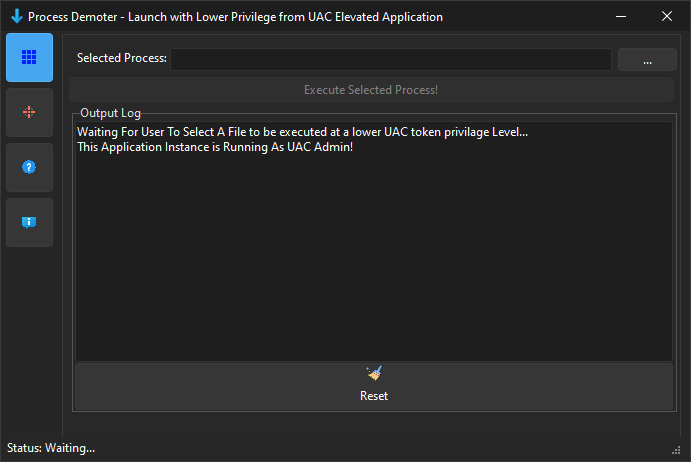
This project illustrates executing applications as non-UAC from a running UAC elevated process.
Unpacker for Launch4j
N-Shield AntiVirus mampu dengan cepat dan akurat mendeteksi file virus, worm, trojan dan lainnya. Pendeteksian dilakukan dengan beberapa metode seperti hash, pattern, heuristic dan generic. Selain itu, N-Shield AntiVirus dapat mendeteksi virus yang memiliki teknologi rootkit
Demonstration of indirect syscall execution techniques
M00N-Crypt is a minimalistic, portable Semi-FUD Crypter.
User Account Control (UAC) is a key part of Windows security. UAC reduces the risk of malware by limiting the ability of malicious code to execute with administrator privileges. This article describes how UAC works and how it interacts with the end-users.
https://github.com/DarkCoderSc/win-brute-logon
Another legacy code for learning purpose. ExeShield is intended to protect a binary (more for commercial apps) by applying a loader/cyper/packer before launching the protected app.
Delphi 7 remote administration tool (RAT) with keylogger, screen capture, file explorer, and diagnostics. Educational security project exploring client-server architecture. Discontinued 2013.
Small program for password and account/login information storage.
A Program for the Extended Option of a Process dump.
Google OTP Integration for Active Directory
A microservice implementing OWASP ASVA v.4 2.1.1 and 2.1.7 passwords-checks for length and commonality