DefenderCheck

Identifies the bytes that Microsoft Defender flags as a threat. Delphi Version
- Active
- Application
- Delphi
- GitHub
- ★ 11


30,079 projects in the catalog.
Free Pascal, Lazarus and Delphi components, libraries and programs from GitHub, SourceForge, Codeberg, GitLab and more. Rate them, mark what looks interesting, and talk about them on their benches.
Identifies the bytes that Microsoft Defender flags as a threat. Delphi Version
An easy to use Drag and drop VCL Windows (WFP) Firewall component!
Go_VM — Delphi Go Source Virtualizer & Obfuscator
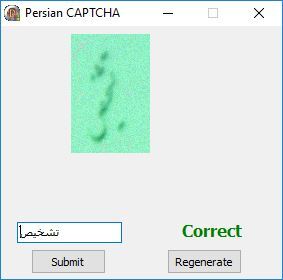
Simple Persian CAPTCHA generator
A simple hook for reverse engineering on x86 processors, to be used with ollydbg, x64dbg and the like.
Delphi library for interacting with the Windows Credential Manager
Yet Another Free Forensic Imager
Tiny Delphi TLS 1.2 implementation for Windows
Windows utility designed to find code caves in x86 and x64 executables for code injection purposes.
Multi user password manager for Linux and windows
Generates Random Serials
Rats sources
Gerador de Captcha para Delphi
Benjamim - JWT library boss for token creation and verification
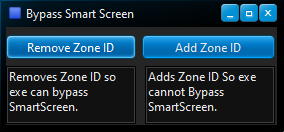
This project shows how to add and remove Zone ID's so that a PE Binary (.EXE) can run without triggering Microsoft Windows Smart Screen.
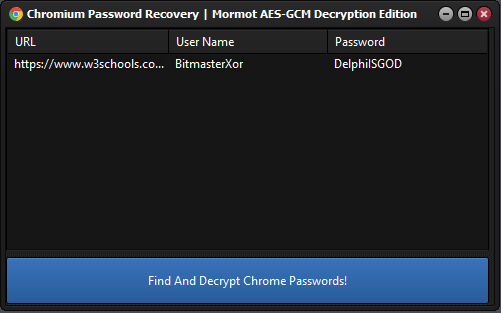
Delphi project showing how to Decrypt Google Chrome Passwords using Mormot V2 Cryptographic library (AES-GCM)
Delphi project to get and Decrypt Chrome encrypted passwords (Works on all chrome based Browsers)
In-memory DLL execution using Reflective DLL Loading
Can read the lock password hash of the ESET AV form the registry and cracks it via bruteforce.
JWT Manager for Delphi
A LCL security system for Lazarus
Password Recovery Tool for USB LockIt
Enigma machine simulator written in Delphi
An EXE Loader That Injects DLL at Entry Point
Regex search filenames, contents, and entropy across all branches in your GitHub repos
Password Recovery for Lock USB Protected Flash Drive
Your Personal Password Manager which avoids using that unreliable Windows Clipboard for typing passwords in the browser
Warez - Patches, Generic Hooks, Keygens and Cracks from releaser and reverse engineer - RadiXX11
An anti debugging technique made in delphi
Обход окна UAC Windows 7 - Windows 10 (RAD Studio XE7)
A mirror of the once public HexLicense repository
ImageHide is simple steganography tool using digital image files.
Malzilla: Malware hunting tool
Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.
NBTempoW V. 2.1 is a forensic tool for making timelines from block devices image files (raw, ewf,physicaldrive, etc.). It uses TSK (The Sleuthkit) and it has been developed with Lazarus V. 1.6.2 ( Delphi compatible cross-platform IDE for Rapid Application Development). It runs only in Windows. If the device image file is splitted, you can select just the first chunk.
red57 Delphi Virus
Console Linux version of the Router Scan
WinAuth to SDA converter
Password Recovery For Wondershare, IDOO, and Gilisoft USB Encryption
用CBuilder自幹Win32的除錯器.(搭配WinAPI)
Sample Delphi code implementing Google Authenticator TOTP
Explorer for Cryptography API: Next Generation
Get auth token from keycloak using native components from Delphi(10.3)
Execute Shellcode
Middleware for Bearer Authentication in HORSE
3 different methods to inject a dll thru a remote thread
Dump LSASS with AV/EDR
Delphi component to access the KeyGen.io API
Welcome to O2, a new way to store and organize your personal data.
PasswordsPro API + libraryes
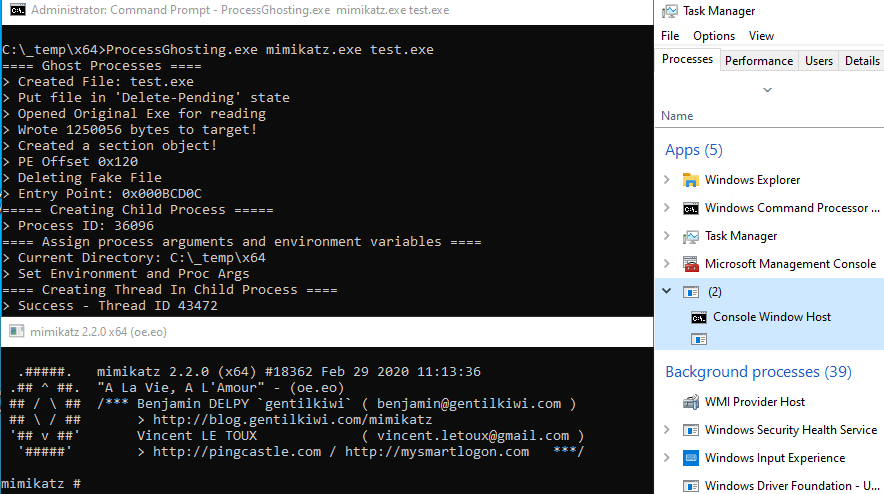
A Process Ghosting PoC written in Delphi
Dump SAM, SYSTEM, SECURITY registry hives from local/remote host
checking ip address for malicious / blacklisting / Spam activity through threat intelligence public feeds
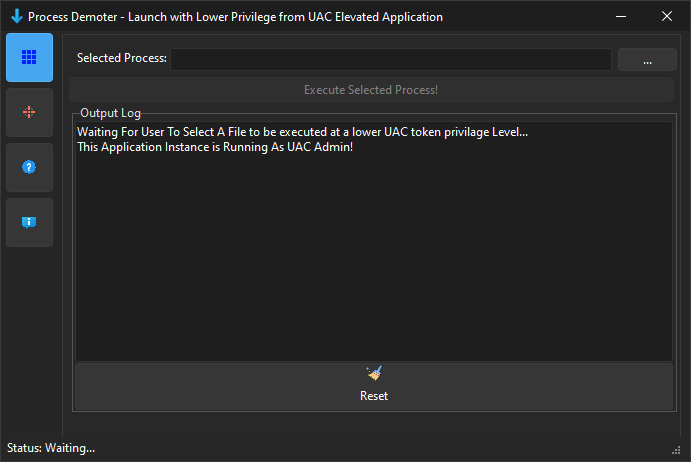
This project illustrates executing applications as non-UAC from a running UAC elevated process.
Windows Hello (fingerprint / face / PIN) user verification for Delphi VCL — a tiny SCUserConsent wrapper