

mORMot2-Cryptography-Demo

mORMot2 Comprehensive Cryptography Demo For Delphi!
- Active · last change 3-10-2026
- ★ 7 on GitHub
README
mORMot V2 Cryptography Demonstration Utility
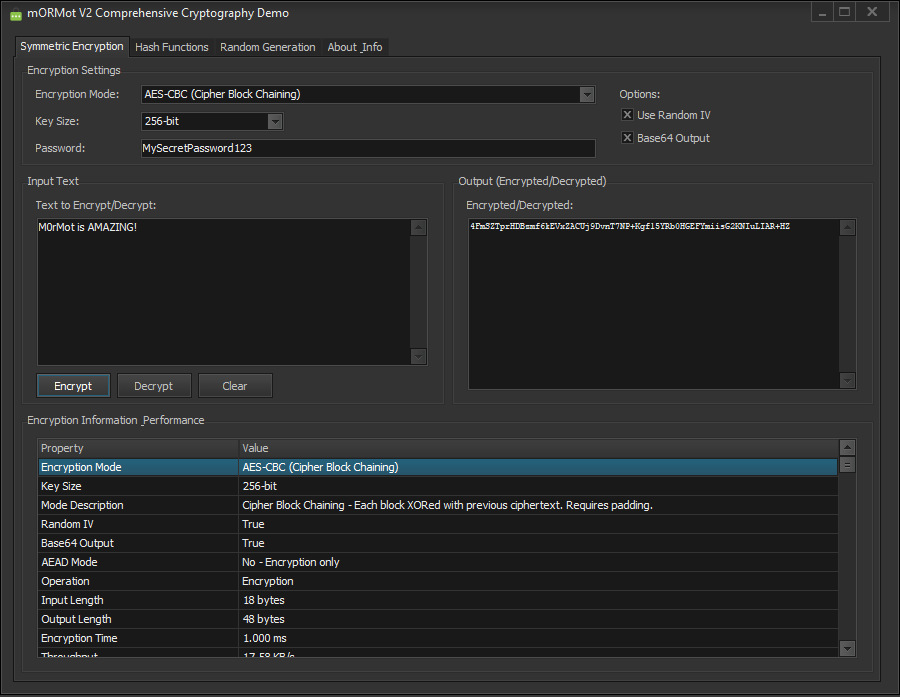
This comprehensive Delphi application showcases the powerful cryptographic capabilities of the mORMot V2 framework. It provides a professional-grade interface for encryption/decryption, hashing, message authentication, key derivation, and secure random number generation.
⚠️ Security Notice
This tool is designed for educational and demonstration purposes. While it implements industry-standard cryptographic algorithms, always review and adapt the code for production use. Pay special attention to key management, salt generation, and iteration counts for PBKDF2.
Features
- AES Encryption Modes: Support for ECB, CBC, CFB, OFB, CTR, GCM, and mORMot custom AEAD modes (CFC, OFC, CTC).
- Variable Key Sizes: 128-bit, 192-bit, and 256-bit AES encryption support.
- Multiple Hash Algorithms: MD5, SHA-1, SHA-256, SHA-384, SHA-512, SHA-3-256, and SHA-3-512.
- HMAC Authentication: HMAC-SHA256 for message authentication and integrity verification.
- PBKDF2 Key Derivation: Password-based key derivation with configurable iterations.
- Secure Random Generation: Cryptographically secure random number generation using TAesPrng.
- Flexible Output Encoding: Base64 or Hexadecimal output formats.
- Performance Metrics: Real-time encryption/decryption speed and throughput measurements.
- Professional Documentation: Extensively commented code with security best practices.
Usage
Encryption/Decryption
- Select Mode: Choose from various AES encryption modes (CBC recommended for general use).
- Set Key Size: Select 128, 192, or 256-bit encryption (256-bit recommended).
- Enter Password: Provide a strong password for key derivation.
- Configure Options: Enable random IV and choose output encoding.
- Encrypt/Decrypt: Enter text and perform encryption or decryption operations.
Hash Functions
- Select Algorithm: Choose from MD5, SHA variants, or SHA-3 (SHA-256 recommended).
- Enter Text: Input the text to be hashed.
- Calculate: Generate the cryptographic hash.
HMAC Authentication
- Set Key: Enter a secret key for HMAC calculation.
- Enter Message: Input the message to authenticate.
- Generate HMAC: Calculate HMAC-SHA256 for verification.
Key Derivation (PBKDF2)
- Enter Password: Provide the source password.
- Set Salt: Enter cryptographic salt (use random salt in production).
- Configure Iterations: Set iteration count (minimum 10,000 recommended).
- Derive Key: Generate the strengthened key.
Random Generation
- Specify Length: Enter desired number of random bytes (1-1024).
- Generate: Create cryptographically secure random data.
Supported Algorithms
Encryption Modes
- AES-ECB: Electronic Codebook (⚠️ NOT RECOMMENDED for production)
- AES-CBC: Cipher Block Chaining (widely supported)
- AES-CFB: Cipher Feedback (stream mode)
- AES-OFB: Output Feedback (stream mode)
- AES-CTR: Counter Mode (fast, parallelizable)
- AES-GCM: Galois/Counter Mode (AEAD - authenticated encryption)
- AES-CFC: mORMot CFB + CRC32C (custom AEAD)
- AES-OFC: mORMot OFB + CRC32C (custom AEAD)
- AES-CTC: mORMot CTR + CRC32C (custom AEAD)
Hash Functions
- MD5: 128-bit (⚠️ cryptographically broken)
- SHA-1: 160-bit (⚠️ deprecated for security)
- SHA-256: 256-bit (✅ recommended)
- SHA-384: 384-bit (high security)
- SHA-512: 512-bit (high security)
- SHA-3-256: 256-bit (latest standard)
- SHA-3-512: 512-bit (latest standard, high security)
Security Best Practices
- Use Strong Passwords: Always use complex, unique passwords for encryption.
- Random IV/Nonce: Always enable random IV for encryption operations.
- Unique Salts: Use a unique random salt for each PBKDF2 operation in production.
- High Iteration Counts: Use at least 10,000 iterations for PBKDF2 (adjust based on security requirements).
- AEAD Modes: Prefer authenticated encryption modes (GCM, CFC, OFC, CTC) when possible.
- Avoid ECB: Never use ECB mode for encrypting multiple blocks of data.
- Key Management: Implement proper key storage and lifecycle management in production.
Technical Requirements
- Delphi: RAD Studio 10.3 Rio or later
- Framework: mORMot V2 (latest version recommended)
- Platform: Windows 32-bit/64-bit
- Dependencies: VCL Components (Forms, Controls, etc.)
Contributing
Contributions are welcome! If you have improvements, security enhancements, or bug fixes, please fork the repository and submit a pull request. All cryptographic implementations should follow established security standards and best practices.
License
This project is provided as is without warranty, use at your own risk! Ensure proper security review before using in production environments.
📧 Contact
Discord: BitmasterXor Made with ❤️ by: BitmasterXor using Delphi RAD Studio