

Code Signing for macOS: what changed
Revision 3 to 4. Removed lines have a minus sign; added lines have a plus sign.
| Old | New | Line | |
|---|---|---|---|
| 1 | 1 | > **Note:** For Apple Notarization requirements for kernel extensions and applications from Mojave 10.14.5 onwards (for kernel extensions from 7 April 2019 and for developers whose first use of their code signing certificate occurred from 7 April 2019) and for all software from Catalina 10.15 onwards that is not distributed via the App Store, see [[Notarization for macOS 10.14.5+]] | |
| 2 | 2 | ||
| 3 | 3 | ## Introduction | |
| 4 | 4 | ||
| 5 | 5 | **[[Code signing]]** ensures both authenticity and integrity of executables that have been downloaded from wide area networks like the Internet. The discussion below applies equally to App Store distribution and distribution outside the App Store. | |
| 6 | 6 | ||
| 7 | 7 | Code signing is required in [[Portal:iOS|iOS]]. On [[Portal:Mac|macOS]] 10.7 and later, it enables programs downloaded from the Internet to be opened without any warnings (if they are signed with an Apple-issued certificate) and it is required when using certain functionality (eg APIs used by debuggers; note that in this case a self-signed certificate that is marked as "trusted" suffices). This functionality is performed by Apple's Gatekeeper software. | |
| 8 | 8 | ||
| 9 | 9 | ## The evolution of Gatekeeper | |
| 10 | 10 | ||
| 11 | 11 | Gatekeeper, first introduced in Mountain Lion (10.8, 2012), is a Mac security feature that was designed to protect Apple computers from malicious software. Gatekeeper checks applications against the list of apps that Apple has approved for its App Store or have been code signed by developers who have Apple-issued certificates where the application is not offered through the app store. It does not perform any safety checks by itself, other than that the application wasn't changed since the developer signed it, nor does it offer any guarantees about the developer other than that they are paying Apple \$US 99 per year (aka an "Identified Developer"). | |
| 12 | 12 | ||
| 13 | 13 | The original Gatekeeper options introduced in Mountain Lion, accessed from Preferences \> Security and Privacy \> General, were: | |
| 14 | 14 | ||
| 15 | 15 | - App Store | |
| 16 | 16 | - App Store and Identified Developers | |
| 17 | 17 | - Anywhere | |
| 18 | 18 | ||
| 19 | 19 | By choosing the **Anywhere** option, the user was once able to entirely disable Gatekeeper. The default setting only allowed the launching of applications from the App Store or from a developer who had signed their application with an Apple-issued certificate. | |
| 20 | 20 | ||
| 21 | 21 | When macOS Sierra was released in 2016, Apple made some important changes to Gatekeeper and limited the the Gatekeeper options to: | |
| 22 | 22 | ||
| 23 | 23 | - App Store | |
| 24 | 24 | - App Store and Identified Developers | |
| 25 | 25 | ||
| 26 | 26 | However, you can restore the missing Gatekeeper *Anywhere*' option in Preferences by opening a terminal and executing the command: | |
| 27 | 27 | ||
| 28 | 28 | $ sudo spctl --master-disable | |
| 29 | 29 | ||
| 30 | 30 | which still works up to and including macOS Catalina. The better, as in more secure, alternative was to instead bypass Gatekeeper by opening the application from the right-click context menu or by control clicking on the application. This still triggered the alert dialog but it now contained an **Open** button to successfully launch the application. This method of bypassing Gatekeeper still works in macOS Catalina, except that on Catalina you need to launch the application a second time with the control-click or right-click to successfully bypass Gatekeeper - the first time you launch the application Gatekeeper cannot be bypassed whether you control-click or right-click or not. | |
| 31 | 31 | ||
| 32 | 32 | ### Big Sur and later on Apple M1 ARM64 processors | |
| 33 | 33 | ||
| 34 | 34 | And then Apple changed the game. | |
| 35 | 35 | ||
| 36 | 36 | When Big Sur is running on an Apple M1 (ARM64) processor, **all native ARM64 code must be signed or the operating system prevents its execution**; and this new Gatekeeper requirement cannot be bypassed by users. Developers can bypass it by running the following command in an Applications \> Utilities \> Terminal window: | |
| 37 | 37 | ||
| 38 | - | ||
| 38 | + | ```text | |
| 39 | 39 | spctl developer-mode enable-terminal | |
| 40 | 40 | ``` | |
| 41 | 41 | ||
| 42 | 42 | and then going to System Preferences \> Security & Privacy \> Privacy, scrolling down until you see an entry for "Developer Tools", authenticate and then tick the checkbox next to Terminal. | |
| 43 | 43 | ||
| 44 | 44 | Intel executables being run under Big Sur on an Apple M1 processor via Rosetta 2 can still be run even though they are unsigned using the control-click or right-click method to bypass Gatekeeper. | |
| 45 | 45 | ||
| 46 | 46 | For more details, see: [[macOS Big Sur changes for developers|Big Sur changes for developers: Code signing - Intel vs M1]]. | |
| 47 | 47 | ||
| 48 | 48 | ## Gatekeeper Dialogs | |
| 49 | 49 | ||
| 50 | 50 | 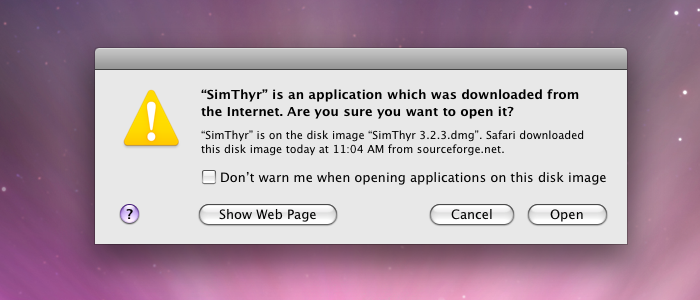 | |
| 51 | 51 | ||
| 52 | 52 | Simple warning after opening a downloaded application in Leopard. | |
| 53 | 53 | ||
| 54 | 54 | 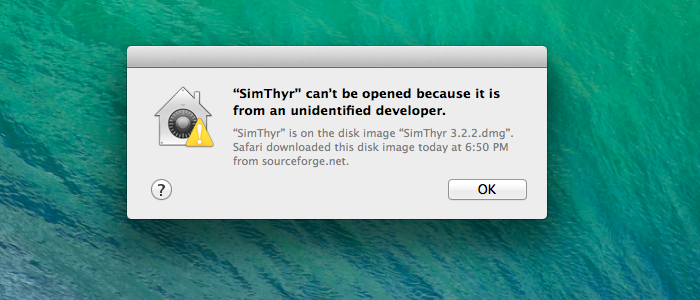 | |
| 55 | 55 | ||
| 56 | 56 | Default settings are more strict in Mavericks, where they prevent downloaded unsigned apps from being started via double-clicking. | |
| 57 | 57 | ||
| 58 | 58 | 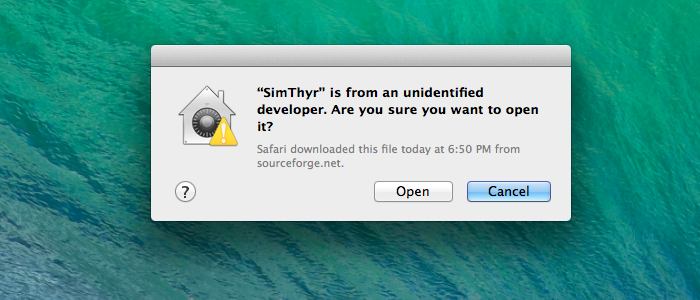 | |
| 59 | 59 | ||
| 60 | 60 | If the application is launched via context menu in Mavericks a simple warning is displayed similar to that of earlier versions. | |
| 61 | 61 | ||
| 62 | 62 | 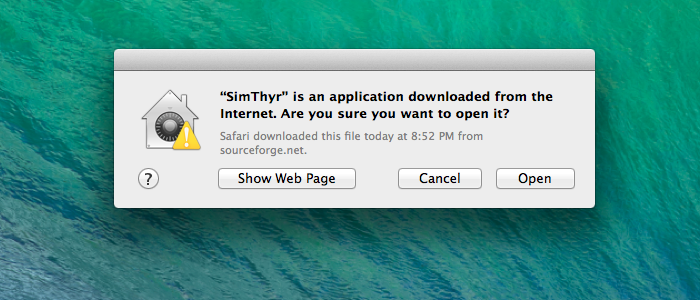 | |
| 63 | 63 | ||
| 64 | 64 | Gatekeeper shows a simplified warning, if a code-signed app has been downloaded and launched for the first time. In subsequent launches the program is starts immediately. | |
| 65 | 65 | ||
| 66 | 66 | 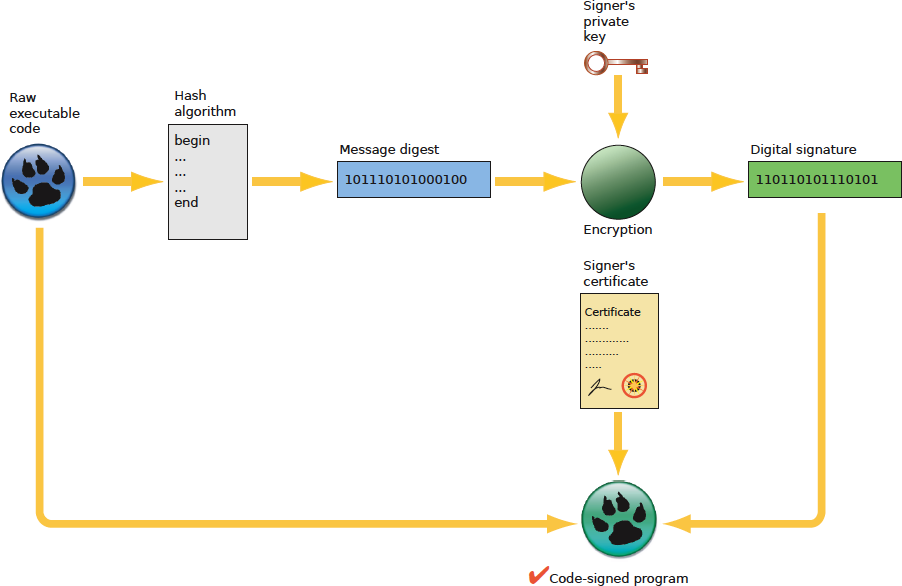 | |
| 67 | 67 | ||
| 68 | 68 | Overview of code-signing a program written with Lazarus and Free Pascal | |
| 69 | 69 | ||
| 70 | 70 | ## Overview | |
| 71 | 71 | ||
| 72 | 72 | The basic steps to sign an application that has been written with Lazarus and/or Free Pascal are: | |
| 73 | 73 | ||
| 74 | 74 | 1. Obtain a Developer ID from Apple and install it in your system's key chain. | |
| 75 | 75 | 2. Note the alphanumeric key of your Developer ID (aka TeamIdentifier). | |
| 76 | 76 | 3. Sign your application with the *codesign* command. | |
| 77 | 77 | 4. Sign your installer pkg with the *productsign* command. | |
| 78 | 78 | ||
| 79 | 79 | It is **not possible** to use certificates from third-party providers like Comodo because they will not pass Gatekeeper which requires an Apple developer issued certificate. Also note that you cannot sign Windows applications with the Apple developer certificate (this time you do need a third-party Comodo etc certificate). | |
| 80 | 80 | ||
| 81 | 81 | A macOS application distributed outside the Mac App Store will generally have 3–4 separate layers of signing: | |
| 82 | 82 | ||
| 83 | 83 | - The application itself will be code signed using an application certificate. | |
| 84 | 84 | - If the application has an installer, the package file will be signed using an installer certificate. | |
| 85 | 85 | - The disk image containing the application or installer will be signed using an application certificate. | |
| 86 | 86 | - The disk image will [[Notarization for macOS 10.14.5+|notarized]], and then the ticket generated by the notary service will be [[Notarization for macOS 10.14.5+|stapled]] to it. | |
| 87 | 87 | ||
| 88 | 88 | ## Gatekeeper requirements | |
| 89 | 89 | ||
| 90 | 90 | - Your application should be standalone with no unacceptable external dependencies. The only acceptable external dependencies are system libraries. All other dependencies should be copied to your MyApp.app bundle folder. Gatekeeper rejects any application that has non-system external dependencies. | |
| 91 | 91 | ||
| 92 | 92 | - All binary files inside MyApp.app should be code signed. | |
| 93 | 93 | ||
| 94 | 94 | - All binary files should be located in standard locations inside the MyApp.app bundle folder. Refer to the table below. | |
| 95 | 95 | ||
| 96 | 96 | | Location | Description | | |
| 97 | 97 | |----|----| | |
| 98 | 98 | | Contents | Top content directory of the bundle | | |
| 99 | 99 | | Contents/MacOS | Main executable; helper apps and tools | | |
| 100 | 100 | | Contents/Frameworks | Frameworks, dylibs | | |
| 101 | 101 | | Contents/PlugIns | Plug-ins, both loadable and extensions | | |
| 102 | 102 | | Contents/XPCServices | XPC services | | |
| 103 | 103 | | Contents/Helpers | Helper apps and tools | | |
| 104 | 104 | | Contents/Library/Automator | Automator actions | | |
| 105 | 105 | | Contents/Library/Spotlight | Spotlight importers | | |
| 106 | 106 | | Contents/Library/LoginItems | Installable login items | | |
| 107 | 107 | | Contents/Library/LaunchServices | Privileged helper tools installed by the ServiceManagement framework | | |
| 108 | 108 | ||
| 109 | 109 | Standard locations for code inside a bundle | |
| 110 | 110 | ||
| 111 | 111 | Note: No non-binary files should ever be located in the folders specified in the table above. | |
| 112 | 112 | ||
| 113 | 113 | ## Using codesign to sign your application | |
| 114 | 114 | ||
| 115 | 115 | **1.** Sign your application with: | |
| 116 | 116 | ||
| 117 | 117 | ``` bash | |
| 118 | 118 | codesign -f -o runtime --timestamp -s "Developer ID Application: YOUR NAME (TEAM_ID)" /path/to/bundle.app | |
| 119 | 119 | ``` | |
| 120 | 120 | ||
| 121 | 121 | **2.** Display basic information about the result of the signing process: | |
| 122 | 122 | ||
| 123 | 123 | ``` bash | |
| 124 | 124 | codesign -dv -r- /path/to/bundle.app | |
| 125 | 125 | ``` | |
| 126 | 126 | ||
| 127 | 127 | If your application was successfully signed this command will return information similar to this: | |
| 128 | 128 | ||
| 129 | 129 | Executable=/Users/apple/Desktop/your.app/Contents/MacOS/yourappname | |
| 130 | 130 | Identifier=org.yourdomain.yourappname | |
| 131 | 131 | Format=app bundle with Mach-O thin (x86_64) | |
| 132 | 132 | CodeDirectory v=20500 size=101470 flags=0x10000(runtime) hashes=3164+3 location=embedded | |
| 133 | 133 | Signature size=9063 | |
| 134 | 134 | Timestamp=7 Dec 2019 at 18:36:08 | |
| 135 | 135 | Info.plist entries=16 | |
| 136 | 136 | TeamIdentifier=<10 alpha numeric digits> | |
| 137 | 137 | Runtime Version=10.14.0 | |
| 138 | 138 | Sealed Resources version=2 rules=13 files=45 | |
| 139 | 139 | designated => identifier "org.yourdomain.yourappname" and anchor apple generic and certificate 1[field.1.2.840.113635.100.6.2.6] /* exists */ and certificate leaf[field.1.2.840.113635.100.6.1.13] /* exists */ and certificate leaf[subject.OU] = <10 alpha numeric digits> | |
| 140 | 140 | ||
| 141 | 141 | **3.** Verify your signature: | |
| 142 | 142 | ||
| 143 | 143 | ``` bash | |
| 144 | 144 | codesign -vv /path/to/bundle.app | |
| 145 | 145 | ``` | |
| 146 | 146 | ||
| 147 | 147 | If your app was successfully signed this command will return the strings "valid on disk" and "satisfies its Designated Requirement", respectively, after the path to your application. | |
| 148 | 148 | ||
| 149 | 149 | ## Using productsign to sign your pkg installer | |
| 150 | 150 | ||
| 151 | 151 | **1.** Sign your installer pkg file with: | |
| 152 | 152 | ||
| 153 | 153 | ``` bash | |
| 154 | 154 | productsign --timestamp --sign "Developer ID Installer: YOUR NAME (TEAM_ID)" /path/to/unsigned.pkg /path/to/signed.pkg | |
| 155 | 155 | ``` | |
| 156 | 156 | ||
| 157 | 157 | **2.** Verify your signature with: | |
| 158 | 158 | ||
| 159 | 159 | ``` bash | |
| 160 | 160 | spctl -vv --assess --type install /path/to/your.pkg | |
| 161 | 161 | ``` | |
| 162 | 162 | ||
| 163 | 163 | which should yield information similar to this if it was successful: | |
| 164 | 164 | ||
| 165 | 165 | your.pkg: accepted | |
| 166 | 166 | source=Developer ID | |
| 167 | 167 | origin=Developer ID Installer: YOUR NAME (<10 alpha numeric digits>) | |
| 168 | 168 | ||
| 169 | 169 | ## Using codesign to sign your disk image | |
| 170 | 170 | ||
| 171 | 171 | Beginning in macOS 10.11.5, you can apply a code signature to read-only, compressed disk images that you use to distribute content. In this case you do not need to separately sign your application. | |
| 172 | 172 | ||
| 173 | 173 | **1.** Sign your disk image with: | |
| 174 | 174 | ||
| 175 | 175 | ``` bash | |
| 176 | 176 | codesign -f -o runtime --timestamp -s "Developer ID Application: YOUR NAME (TEAM_ID)" /path/to/YourImage.dmg | |
| 177 | 177 | ``` | |
| 178 | 178 | ||
| 179 | 179 | **2.** Verify your signature with: | |
| 180 | 180 | ||
| 181 | 181 | ``` bash | |
| 182 | 182 | spctl -a -t open --context context:primary-signature -vv /path/to/YourImage.dmg | |
| 183 | 183 | ``` | |
| 184 | 184 | ||
| 185 | 185 | which should yield information similar to this if it was successful: | |
| 186 | 186 | ||
| 187 | 187 | YourImage.dmg: accepted | |
| 188 | 188 | source=Developer ID | |
| 189 | 189 | origin=Developer ID Application: YOUR NAME (<10 alpha numeric digits>) | |
| 190 | 190 | ||
| 191 | 191 | **After 3 February 2020 Apple is fully enforcing notarization** for macOS 10.14.5+ (Mojave) with the consequence that the above verification of your disk image will now return information similar to this: | |
| 192 | 192 | ||
| 193 | 193 | YourImage.dmg: rejected | |
| 194 | 194 | source=Unnotarized Developer ID | |
| 195 | 195 | origin=Developer ID Application: YOUR NAME (<10 alpha numeric digits>) | |
| 196 | 196 | ||
| 197 | 197 | See [[Notarization for macOS 10.14.5+]] for more details. | |
| 198 | 198 | ||
| 199 | 199 | ## Updating a signed file | |
| 200 | 200 | ||
| 201 | 201 | Whenever you update a signed file, create a new file. Do not copy a new signed file over an old signed file. | |
| 202 | 202 | ||
| 203 | 203 | Specifically, the code signing information (code directory hash) is hung off the vnode within the kernel, and modifying the file behind that cache will cause problems. You need a new vnode, which means a new file, that is, a new inode. Documented in WWDC 2019 Session 703 All About Notarization - see [slide 65 (PDF)](https://devstreaming-cdn.apple.com/videos/wwdc/2019/703yqvyjv9mi5ur6/703/703_all_about_notarization.pdf). | |
| 204 | 204 | ||
| 205 | 205 | ## Ad hoc signing | |
| 206 | 206 | ||
| 207 | 207 | This is especially important on ARM64 M1 Apple processors which require all native code to be validly signed (if only ad hoc) or the operating system will not execute it, instead killing it on launch. To ad hoc sign an application: | |
| 208 | 208 | ||
| 209 | - | ||
| 209 | + | ```text | |
| 210 | 210 | codesign --force --deep -s - lazarus.app | |
| 211 | 211 | ``` | |
| 212 | 212 | ||
| 213 | 213 | or to ad hoc sign an executable file: | |
| 214 | 214 | ||
| 215 | - | ||
| 215 | + | ```text | |
| 216 | 216 | codesign --force -s - lazarus | |
| 217 | 217 | ``` | |
| 218 | 218 | ||
| 219 | 219 | A single dash/hyphen on its own for the identity makes it an ad hoc signature with no certificate. | |
| 220 | 220 | ||
| 221 | 221 | You can check the validity of an ad hoc signed executable with: | |
| 222 | 222 | ||
| 223 | - | ||
| 223 | + | ```text | |
| 224 | 224 | codesign -dv -r- lazarus | |
| 225 | 225 | ``` | |
| 226 | 226 | ||
| 227 | 227 | which should produce output similar to the below: | |
| 228 | 228 | ||
| 229 | - | ||
| 229 | + | ```text | |
| 230 | 230 | Executable=/Users/trev/lazarus-src/lazarus | |
| 231 | 231 | Identifier=lazarus | |
| 232 | 232 | Format=Mach-O thin (arm64) | |
| 233 | 233 | CodeDirectory v=20400 size=336137 flags=0x2(adhoc) hashes=10498+2 location=embedded | |
| 234 | 234 | Signature=adhoc | |
| 235 | 235 | Info.plist=not bound | |
| 236 | 236 | TeamIdentifier=not set | |
| 237 | 237 | Sealed Resources=none | |
| 238 | 238 | # designated => cdhash H"2e6f474452344d6fa42feee3db14a05c14d595a3" | |
| 239 | 239 | ``` | |
| 240 | 240 | ||
| 241 | 241 | In cases where you have compiled the executable yourself, the macOS linker will ad hoc sign the executable for you in which case you need do nothing. You can check the validity with the command above in which case the CodeDirectory output line will indicate that the linker signed the executable with an ad hoc signature as follows:: | |
| 242 | 242 | ||
| 243 | - | ||
| 243 | + | ```text | |
| 244 | 244 | CodeDirectory v=20400 size=336032 flags=0x20002(adhoc,linker-signed) hashes=10498+0 location=embedded | |
| 245 | 245 | ``` | |
| 246 | 246 | ||
| 247 | 247 | ## Code signing an x86_64 binary on an aarch64 machine | |
| 248 | 248 | ||
| 249 | 249 | ## How to install certificates on a second computer | |
| 250 | 250 | ||
| 251 | 251 | There are two ways to do this: | |
| 252 | 252 | ||
| 253 | 253 | 1. using the Keychain Access application; and | |
| 254 | 254 | 2. using Xcode. | |
| 255 | 255 | ||
| 256 | 256 | ### Using the Keychain Access application | |
| 257 | 257 | ||
| 258 | 258 | - On the first computer which has the certificates, open the Keychain Access application and create a new keychain. Now select your existing login keychain, and then My Certificates. Your certificates should be shown on the right. There should be a disclosure arrow on the left side, and selecting that should reveal your private key. Select each certificate, and copy and paste (do not drag or you'll remove it from your login keychain) it into your new keychain. | |
| 259 | 259 | ||
| 260 | 260 | - Copy the newly created keychain from your first computer to your second computer, open it with the Keychain Access application and copy/paste/drag the certificate to your second computer's login keychain. | |
| 261 | 261 | ||
| 262 | 262 | ### Using Xcode | |
| 263 | 263 | ||
| 264 | 264 | - On the first computer which has the certificates, open Xcode and go to Preferences \> Accounts, select your account, select the gear symbol in the bottom left, choose Export Apple ID and Code Signing Assets, and then save the file. | |
| 265 | 265 | ||
| 266 | 266 | - Copy the developer profile file you saved on your first computer to the second computer, open Xcode, go to Preferences \> Accounts, select your account, select the gear symbol in the bottom left, and then choose Import Apple ID and Code Signing Assets. | |
| 267 | 267 | ||
| 268 | 268 | ## How to check what certificates are installed | |
| 269 | 269 | ||
| 270 | 270 | Once you have created or imported the certificates on your computer, you can check for their presence by opening an Applications \> Utilities \> Terminal and executing the following command: | |
| 271 | 271 | ||
| 272 | - | ||
| 272 | + | ```text | |
| 273 | 273 | $ security find-identity -p basic -v | |
| 274 | 274 | ``` | |
| 275 | 275 | ||
| 276 | 276 | This command will list all available certificates on this computer. Make sure that you can see the presence of the *Developer ID Application* and *Developer ID Installer* certificates. If you are a member of more than one team, you may see multiple certificates for each team. | |
| 277 | 277 | ||
| 278 | 278 | You can identify the certificates by the hexadecimal number or by the descriptive name, eg "Developer ID Application: Your Name (AB123456DE)" | |
| 279 | 279 | ||
| 280 | 280 | The ten character alpha-numeric code at the end of your name is your Developer Team ID. If you are a member of multiple developer teams, you will have multiple certificates and the team ID will help you distinguish them. | |
| 281 | 281 | ||
| 282 | 282 | ## See also | |
| 283 | 283 | ||
| 284 | 284 | - [[macOS Big Sur changes for developers|Code signing: Intel vs Apple Silicon]] | |
| 285 | 285 | - [[Apple Developer Certificates]] | |
| 286 | 286 | - [[Notarization for macOS 10.14.5+]] | |
| 287 | 287 | - [[Hardened runtime for macOS]] | |
| 288 | 288 | - [[Sandboxing for macOS]] | |
| 289 | 289 | - [[Signing and Notarization FAQ]] | |
| 290 | 290 | - [[macOS Gatekeeper Debugging Tips]] | |
| 291 | 291 | ||
| 292 | 292 | ## External links | |
| 293 | 293 | ||
| 294 | 294 | - [Apple Developer portal](https://developer.apple.com/) | |
| 295 | 295 | - [Apple: Code Signing Overview](https://developer.apple.com/support/technical/code-signing/) | |
| 296 | 296 | - [Apple: Code Signing Guide](https://developer.apple.com/library/mac/documentation/Security/Conceptual/CodeSigningGuide/) | |
| 297 | 297 | - [Apple: TN2206 - macOS Code Signing In Depth](https://developer.apple.com/library/archive/technotes/tn2206/_index.html) | |
| 298 | 298 | - [Apple: Code signing x86_64 binaries on aarch64](https://developer.apple.com/forums/thread/673323). | |
| 299 | 299 | ||
| 300 | 300 | --- | |
| 301 | 301 | *From the Free Pascal wiki, page "Code Signing for macOS", as it stood on 2022-02-13 after a change by Trev, out of the wiki's dump of 2024-05-26. Copyright stays with the author who wrote it, according to the old wiki's [[Licensing]] page. If you have concerns about this material, [message the admin](/wiki-contact).* |